Generate Portworx Backup Spec
Use the Portworx Central portal to generate the Portworx Backup spec. The generated spec (the values-px-central.yaml file and the pxc-credentials secret) is used by both the Helm and Argo CD installation methods.
Before you generate the Portworx Backup spec, make sure you have completed the installation environment setup.
The steps below apply to both internet-connected and air-gapped environments; air-gapped-specific values are called out inline where they diverge.
Portworx Backup installation requires configuring passwords for various database components. Ensure that you follow the password guidelines listed in the Password Policy section.
Generate the Portworx Backup spec
To generate the Portworx Backup spec for the required version of Portworx Backup:
-
Access Portworx Central SpecGen.
-
Enter user credentials and make sure that you go through End-User License Agreement (EULA).
If you are new to Portworx Central, click Create account to generate your login credentials. You can also sign in with your organization’s OIDC identity provider, Google, or GitHub account.
-
Click Sign In to access the Portworx Central portal.
-
In the Spec Details tab provide the following values:

-
Release Information
- Backup Version: select the required version of Portworx Backup from the drop-down list
- Namespace: provide the name of the namespace where you want an instance of Portworx Backup to be installed
- Select Cluster Platform: select your cluster platform from the drop-down list. Refer Requirements for supported platforms.
- Select Deployment Architecture: choose Classic to install Portworx Backup as a standalone instance managing its own backup operations independently. For information on installing in Federated mode, see Install Portworx Backup in Federated Mode.
-
Configuration
-
StorageClass Name: Enter the StorageClass name. See the tooltip for details.
noteDefining the namespace and StorageClass is a one-time configuration step that should be completed during the initial installation. PVCs will be created using Namespace and StorageClass values you define in the SpecGen, and these values cannot be modified later during an upgrade.
-
Enable Rancher RBAC: select this checkbox if you are using Rancher for managing your Kubernetes clusters and want to enable Rancher's Role-Based Access Control (RBAC) for Portworx Backup. This feature can be enabled only if you have LDAP or PingIdentity as your identity provider. For more information, see Portworx Backup Rancher RBAC and Rancher RBAC.
-
Use your OIDC: select this checkbox if you want to integrate an external OIDC-compliant identity provider (such as Auth0, Keycloak, Okta, or Azure AD) and key in the following fields:
- Endpoint
- Client ID
- Client Secret
These values can be obtained from your identity provider's configuration. For more information on integrating external authorization providers, see Integrate Auth Providers
-
Use existing Prometheus: select this checkbox if you have to use your existing Prometheus stack to monitor Portworx Backup and enter the values for the following fields. For detailed instructions on configuring your own Prometheus, see Configure Observability with your own Prometheus.
- Prometheus Endpoint: enter details of the endpoint where your Prometheus is installed
- Alertmanager Endpoint: enter details of the endpoint where your Alertmanager is installed
- Prometheus secret name: enter secret name of your Prometheus stack
- Alertmanager secret name: enter secret name of your Alertmanager
- Use Custom email template from PX-Backup: select to upload the Portworx Backup custom email template to your pre-configured Alertmanager for email notifications
cautionA cluster-wide (global) Prometheus operator can conflict with the Prometheus and Alertmanager instances that Portworx Backup manages in the
<pxb-namespace>namespace, driving those pods intoCrashLoopBackOff. If you run a cluster-wide Prometheus operator, exclude the Portworx Backup namespace from it before installing. For details, see Prometheus requirements.By default, the persistent volume size for the Prometheus server is 5 GB. If you need more storage, append the following to the generated Helm install command:
--set persistentStorage.prometheus.storage=8Gi,persistentStorage.prometheus.retentionSize=7360MBThis example sets the Prometheus server's persistent volume size to 8 GB and its retention size to 7360 MB. Set the storage based on your needs, and set
retentionSizeto about 92% of your chosenprometheus.storagevalue, expressed in MB (for example,7360MBfor8Gi). -
Proxy Configuration: select this checkbox if you have proxy server configured in your environment and enter the values for the following fields:
-
Unauthenticated: choose this if you have unauthenticated proxy server.
- HTTP Proxy: proxy server URL for http proxy
- HTTPS Proxy: proxy server URL for https proxy
- NO PROXY: comma separated list of hostnames, IPs, or domains that should bypass the proxy settings
-
Authenticated/CA: choose this option if your cluster is behind a proxy server with authentication or CA
- Proxy configuration secret: name of the Kubernetes proxy configuration secret holding the proxy configuration. Create this secret in the namespace where you install Portworx Backup (the Namespace value you set above in Release Information, for example
central).
- Proxy configuration secret: name of the Kubernetes proxy configuration secret holding the proxy configuration. Create this secret in the namespace where you install Portworx Backup (the Namespace value you set above in Release Information, for example
-
-
Enable Telemetry: select this checkbox to enable telemetry and upload Portworx Backup usage data to Pure1. When enabled,
--set telemetry.enabled=trueis appended to the generated Helm install command. For more information, see Configure Telemetry.
-
-
(For air-gapped environment only) Under Custom Registry, select Use custom registry checkbox and provide the following values:

- Custom Image Repository Location: path of custom image repository. For more information, see Set up the environment.
- Image Pull Secret(s): create a secret in the following cases:
- If image pulling from an internal repository requires credentials
- If you were using
docregistry-secret
-
Database Credentials: This section configures database passwords for the various database components used by Portworx Backup. For more information on password guidelines, see Password Policy.
- MySQL Root User Password: root password for MySQL database
- Postgres User Password: password for PostgreSQL user
- MongoDB PX-Backup User Password: password for MongoDB PX-Backup user
- MongoDB Root User Password: root password for MongoDB database
- MongoDB Replica Set Key: key for MongoDB replica set authentication
- Encrypt MongoDB: select this checkbox to enable encryption at rest for MongoDB database
- MongoDB Master Encryption Key: Master encryption key for MongoDB encryption at rest
cautionSafeguarding your encryption key is vital to prevent permanent data loss. If the key is lost, you will be unable to access your encrypted data, as it is the only means of decryption. Without it, the data is rendered completely inaccessible and cannot be recovered. Note that encryption keys cannot be rotated after they are set.
-
-
Click Next to view the Finish tab, which provides the list of commands needed to complete the installation of Portworx Backup in your environment.
-
In the Finish tab, copy the YAML under Step 1 to your terminal and run it to create a Kubernetes secret containing database credentials and configuration parameters for Portworx Backup components.
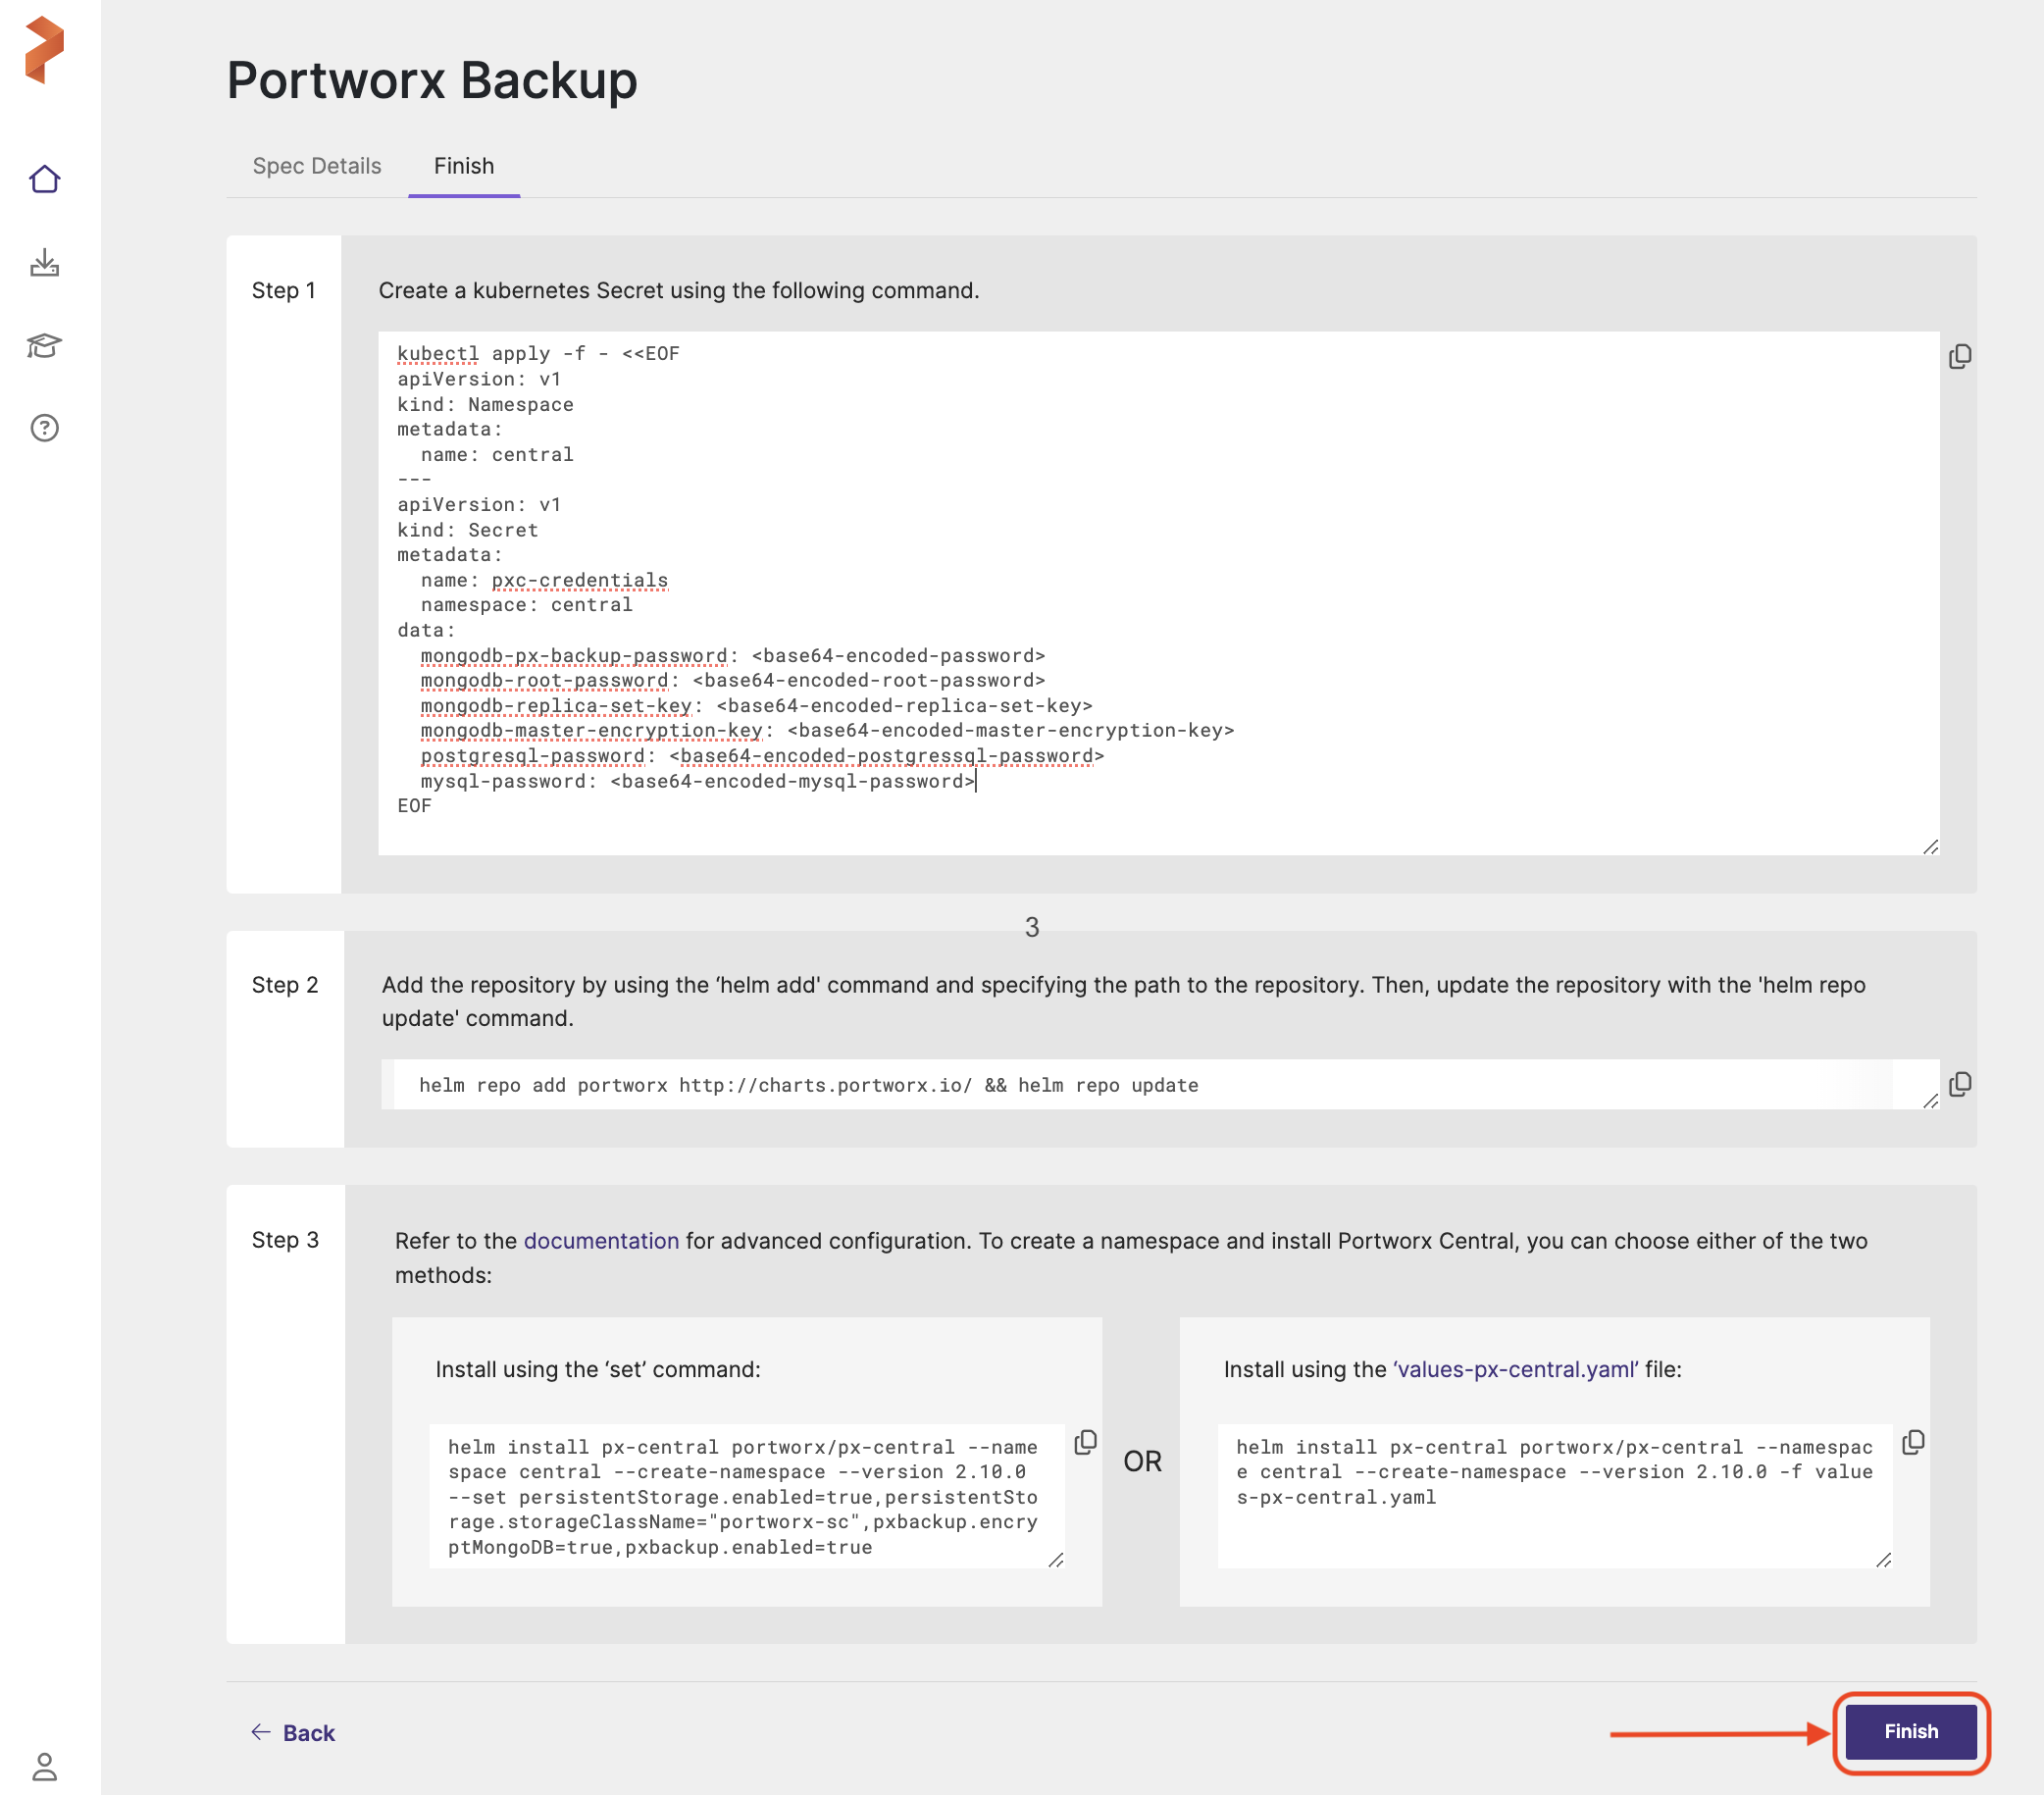
The command creates the specified namespace (for example,
central) and generates apxc-credentialssecret containing database passwords. The database credentials include password, replica set, and encryption key for MongoDB, and only passwords for PostgreSQL and MySQL components of Portworx Backup.cautionThe values in a Kubernetes
Secretare only base64-encoded and not encrypted. Anyone who can read the Secret (or the command output in your terminal or shell history) can trivially decode them. Base64 encoding is not a security control. Protect these credentials with proper Kubernetes access controls and platform protections: restrictget/liston Secrets in this namespace with RBAC, enable encryption at rest (ideally backed by a KMS provider) for Secrets in your cluster, and avoid echoing or storing the plaintext passwords in logs, shell history, or source control.If the
pxc-credentialssecret is not set, installing Portworx Backup fails with the following error:time="<UTC Timestamp>" level=fatal msg="Pre-install Hook failed: RunPreInstall: failed to validate custom passwords: ValidateCustomPasswordSecret: error validating pxc-credentials secret: secret pxc-credentials not found in namespace central" -
Verify that the secret was created correctly before starting the Helm or Argo CD installation:
# Confirm the secret exists in the target namespacekubectl get secret pxc-credentials -n <pxb-namespace># Confirm it contains the expected keys (do not print the decoded values)kubectl get secret pxc-credentials -n <pxb-namespace> -o jsonpath='{.data}' | tr ',' '\n'Confirm the secret exists in the namespace you install into and that access is restricted to the intended service accounts (review the RBAC
Role/RoleBindingthat grantgeton Secrets in this namespace). If the secret is missing or in the wrong namespace, the install fails with thepxc-credentials secret not founderror shown above — recreate it from the Finish tab before continuing.Keep the Finish tab open. In the next step, when you install Portworx Backup using Helm, you use the commands from the Finish tab: Step 2 adds the Portworx Helm repository, and Step 3 provides the Helm install command.
What to do next
Install Portworx Backup using the generated specs and the pxc-credentials secret through either of the following methods: